
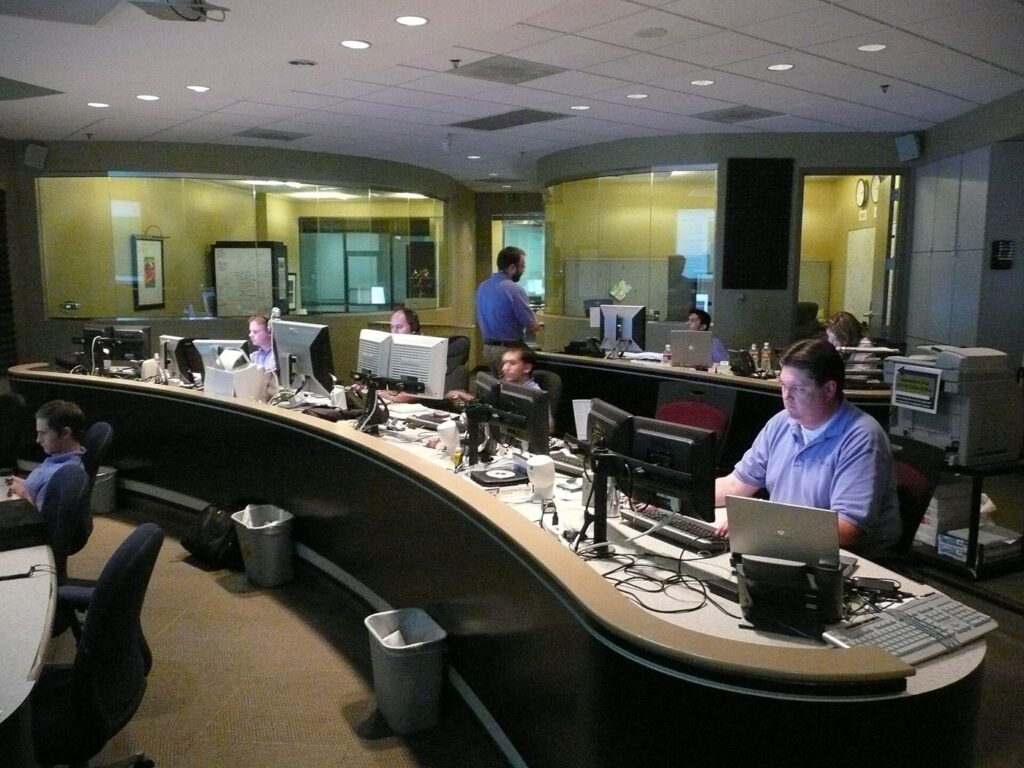
Hospitals are strengthening their cyber defences after a series of attacks showed how quickly a digital incident can disrupt appointments, diagnostics and emergency care. Security operations centres that monitor hospital networks around the clock are now watching not only conventional computer systems, but also connected medical devices, building controls and remote access used by clinical staff. Analysts say the goal is to spot unusual behaviour early, isolate affected systems and keep essential services running while an investigation continues. That work requires close coordination with doctors and managers, because shutting down a compromised system may protect data but could also delay treatment. Hospitals are therefore rehearsing incident plans in the same way they practise fire drills, with clear decisions about which services can move to backup systems or paper processes. The sector’s challenge is funding and staffing, since experienced cyber specialists are in short supply and hospitals compete with banks and technology firms for the same talent.
What the Evidence Shows
A growing response is to share defence across groups of hospitals, pooling monitoring staff, threat intelligence and recovery expertise that no single site could afford alone. Specialists following hospital cyber defence operations say that shared centres can watch for attack patterns across many networks at once, warning others before the same technique spreads. They also stress that basic hygiene still prevents many incidents, including prompt patching, strong authentication and segmented networks that stop an intruder moving freely. Suppliers are under pressure too, as hospitals demand clearer security standards for the software and devices they buy. When attacks do succeed, transparent communication with patients and regulators is becoming part of the recovery plan, rather than an afterthought. The lesson from recent incidents is that cyber security is now patient safety work, deserving the same planning, rehearsal and investment as any other clinical risk. Reporting and analysis from sources such as Wired track the same developments, and specialists following hospital cyber defence operations say the direction is now consistent across independent lines of evidence.
The Wider Context
The wider context is an industry learning to ship capability and restraint together. Products built around hospital cyber defence operations now launch with safety evaluations, usage data and rollback plans as standard, because enterprise buyers and regulators ask for them in the first meeting. Companies that treated those questions as friction are discovering they have become the purchase criteria.
What Happens Next
What happens next for hospital cyber defence operations depends less on another breakthrough than on the unglamorous work of reliability, pricing and support. The buyers evaluating it now are not enthusiasts; they are operators with budgets and auditors, and their checklists will decide the timeline. On the evidence of the current pilots, the technology has earned the right to be judged by them. You can follow related developments in our coverage of technology.
None of this will be settled by a single announcement, study or product launch. The pattern to watch is accumulation: independent confirmations, honest reporting of failures and steady improvement in the underlying numbers. Readers who follow those signals, rather than the loudest claim of the week, will understand this subject better than most of the commentary surrounding it suggests is possible.
